All posts by Adam Thompson

Stepwise Guide on How to Install an SSL Certificate on Lotus Domino

SSL Certificate Installation Guideline on Lotus Domino

There are several guides available on the Internet about ‘How to install an SSL certificate on Lotus Domino’, but given the steps involved, the process sometimes tends to confuse the users, especially the first-timers. So, we’ve created an SSL installation guide, which is both detailed and at the same time very easy to understand.

Read More Stepwise Guide on How to Install an SSL Certificate on Lotus Domino

SSL Encryption: A Mandatory Aspect for Cloud Computing Security

Enable Cloud Computing Security with SSL Certificates Encryption

With the ever-evolving field of Information Technology, the innovative concepts that make our lives simpler never cease to amaze us. Cloud Computing happens to be one of the recent such examples, in spite of being in its infancy period, it has rapidly changed the IT landscape.

Read More SSL Encryption: A Mandatory Aspect for Cloud Computing Security

Shellshock: A Vulnerability More Serious Than Heartbleed?

Understand Vulnerabilities and Their Causes to Secure Website

The hits just keep on coming! We have yet again bumped into another software bug that threatens our web security. It has been hardly 5 months since the discovery of the ‘Heartbleed’ bug and now another nasty surprise has been uncovered, called ‘Shellshock’.
shellshock bug

What is the Shellshock Bug?

The Shellshock bug is the latest vulnerability that is likely to affect several versions of Linux and Unix operating systems. This was discovered by Linux expert Stéphane Chazelas on September 2014 in the UK. Linux-based web routers having web interface (using Common Gateway Interface) are also found to be vulnerable to Shellshock.

Alternately known as the Bash Bug, Shellshock is likely to be more severe compared to the Heartbleed Bug. As per the security experts, attackers can easily exploit the bug in the Bash and take complete control of the system being targeted. The United States Computer Emergency Readiness Team (US-CERT) of the Department of Homeland Security has issued an alert about this vulnerability affecting the Unix-based operating systems such as Linux along with Apple’s Mac OSX.

How Does Shellshock Bug Attacks?

A remote attacker can easily exploit Bash under definite circumstances. The attacker just needs to manage to force an application for sending a malicious environment variable to the bash.

Attackers are most likely to choose the route via web servers using the Common Gateway Interface (CGI), which is the most popular system used for creating dynamic web content. But, attackers tend to use it or exploit it to send malicious environment variable to the target system. As the Bash is used by the server for interpreting the variable, automatically it will also run the malicious command that was inserted.

The following diagram depicts how a malicious command can be injected at the end of a legitimate environment variable, which is later run by Bash.
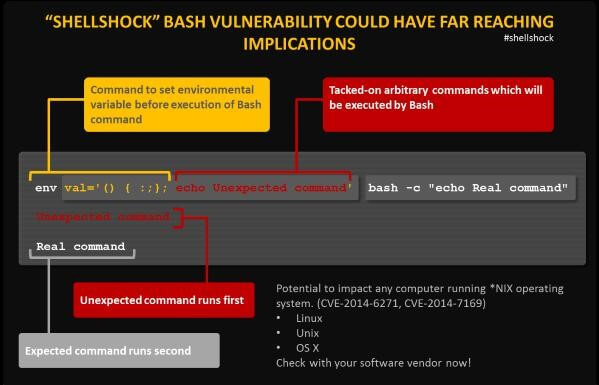
shellshock bug table

Serious consequences follow, once an attacker is successfully able to exploit this vulnerability on a server. It may allow attackers to download harmful malware on the targeted computers or dump password files. Similarly, attackers can also compromise and attack other devices in the network after entering the firewall of the victim’s computer.

Why Shellshock is projected to be more harmful than Heartbleed

The severity of the aftermath caused by this bug can be understood only after highlighting the importance of the element it affects, the Bash.

To be precise, the vulnerability caused by Shellshock affects the UNIX Bash Shell. Bash, also known as Shell, is the common component of several versions of Linux and UNIX. The function of Bash is to perform as the command language interpreter, which means it allows the users to type the command in a simple text-based window that the operating system can run.

Bash is also used to run the commands, which are passed on by the applications. This happens to be the very feature that is exploited by the Shellshock bug. These environment variables are very dynamic, named values that directly affect how the processes are run on a computer. So, the weakness being exploited here is that the attacker can easily introduce a malicious code on to the environment variable, which will be run after the variable is received.

On the Common Vulnerability Scoring System (CVSS), Shellshock has received a straight 10/10, which makes it one of the biggest and most notorious bugs we have seen in the history of the Internet. And looking at the immense presence of the Bash shell, a large number of internet devices shall end up being vulnerable to Shellshock such as routers, Linux systems, Macs, web servers etc.

Apparently, Bash is the most widely used software in web servers at various organizations. Shellshock enables cyber criminals to attack a web server with the convenience of remote access to compromise the host. Once the victim organization is compromised, an attacker can completely take over the system, unlike Heartbleed – a bug in OpenSSL, where attackers could just spy on computers and not take the control of the system completely.

Procedure to Check your Computer’s Vulnerability

Rather than fretting about when and how your computer is going to get affected by Shellshock, it is advisable to find out for real if or not your computer is vulnerable to this bug. Here is a little procedure for that:

  1. Open the terminal on your computer and run the following command:
    env x='() { :;}; echo vulnerable' bash -c "echo this is a test"
  2. You will see the following, if your system is vulnerable to the Bash:
    vulnerable
    this is a test
  3. However, if your system is well-patched and protected, you will see the following message being flashed:
    $ env x='() { :;}; echo vulnerable' bash -c "echo this is a test" bash: warning: x: ignoring function definition attempt bash: error importing function definition for `x' this is a test

Tips to Reduce the Risks of a Shellshock bug

Users can follow the tips mentioned here to reduce the risks of falling prey to this bug:

Online Businesses: All users of Linux/Unix-based systems are recommended to implement the patches immediately. The following are a few patches that have been released by their respective vendors:

Please note, Red Hat has updated its advisory for Shellshock after noting that its initial patch is incomplete.

Consumers: For consumers, it is advisable to apply patches to the routers and any other web-enabled devices, as and when the vendors provide them.

However, if the patch is not yet released for a particular Linux/ Unix, it is recommended to shift to an alternate shell till a proper patch is provided by the vendor.

SHA-2 Algorithm – A Revolution For Better Website Security

Understand SSL Industry Big Changes SHA-2 Algorithm

It seems SHA-2 algorithm is efficiently revolutionizing the Internet Security scene. All the big names from the industry are now rooting for SHA-2 and deprecating their support towards SHA-1, the predecessor of SHA-2. So, let’s have a look at why and how this SHA-2 revolution is taking place.

Read More SHA-2 Algorithm – A Revolution For Better Website Security

Google to Exclude SHA-1 in the Upcoming Chrome Browsers

Understand SHA-1 Algorithm Weakness As Per Google Standards

The software giant Google© has made a crucial decision about deprecating SHA-1 signature algorithm in their extremely popular Chrome browser in order to strengthen the security of the Internet.

Google© has always taken strong actions when it comes to users’ data protection on the Internet. This time, for the sake of Internet security, they have planned to stop trusting the SHA-1 algorithm, which might be susceptible to several cyber-attacks due to inability to keep up with the latest techniques used by the hackers. Google© has been putting in the best efforts to build secure measures for its users.

So it looks like it is finally about time to say good bye to the SHA-1 signature algorithm due to this major modification from Google. So, let’s take a quick look at these changes and how the users need to manage website security based on these developments.

  • What is SHA-1 signature algorithm?

    SHA stands for “Secure Hash Algorithm” and the version SHA-1 works on the single hash function, which is known to be vulnerable according to many web security experts.

  • What is SHA-2 signature algorithm?

    SHA-2 is the latest version in SHA Algorithm history, and it is the next generation SHA-2 signature algorithm, which includes multiple hash functions to protect user’s data while exchanging them on the Internet.

  • Is it safe to use SHA-1?

    The vulnerabilities of SHA-1 are very well known and have been demonstrated many times over. In a practical live environment, it is still safe to use the SHA-1 signature algorithm. However, as per critics and SSL experts, SHA-1 will create security vulnerabilities in near future on the Internet. For that reason, best practices do not recommend SHA-1.

  • What if my existing SSL certificate is SHA-1?

    If your certificate is based on SHA-1 algorithm, it is very easy to get it exchanged for a SHA-2 certificate. All you need to do is re-issue your SSL certificate by choosing the algorithm as SHA-2.

  • Which Certificate Authorities (CAs) have this new SHA-2 algorithm?

    There are plenty of SSL certificate vendors on the Internet but it gets very difficult to find out exactly which CA has migrated all its SSL certificates and Code Signing Certificates to SHA-2 signature algorithm. We have carried out a little research on this and found that Symantec™, GeoTrust®, Thawte™, and RapidSSL™ offer Low Price SSL certificates with SHA-2 algorithm and technical support by the team of experts.

  • What is the difference between SHA-1 and SHA-2 algorithm?

    SHA-1 signature algorithm works on a single 128-bit hash function, whereas SHA-2 signature algorithm works on multiple hash functions.
    SHA-2 signature algorithm is stronger than SHA-1 because it has multiple hash function such as SHA-224, SHA-256, SHA-384, SHA-512, SHA-512/224, SHA-512/256 and out of them SHA-256 bit is widely established and more demanded hash function algorithm. The suffix numbers indicate bit length. So SHA-2’s full set of functions are higher bit-length than SHA-1 and therefore are more secure.

  • What is Google’s preparation for the elimination of SHA-1?

    Here is how the upcoming versions of the Google Chrome browser shall react to a SHA-1 SSL certificate.

  • Chrome 39 – Public release in early November 2014

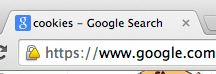
    Websites secured by SHA-1 certificates that expire in 2017 or later, on this version will be treated as ‘Secure, but with minor errors’. A small yellow triangle on the padlock will be displayed on the URL as shown below:

    chrome version 39 error

  • Chrome 40 – Branch Point – November 7 2014 & Stable after Holiday Season

    Websites with SHA-1 SSL certificates expiring between June 1 2016 to December 31 2016 will trigger the ‘Secure, but with minor errors’ warning as mentioned above.

    And the websites secured with SHA-1 SSL certificates expiring on or after January 1 2017, will be treated as ‘neutral, lacking security’. In this, the padlock will be replaced by a blank page icon, as shown in the image below:

    chrome version 40

  • Chrome 41 – Branch Point – Q1 2015

    All the websites relying on SHA-1 SSL certificates expiring between January 1 2016 to December 31 2016 will trigger the ‘Secure, but with minor errors’, as described above.

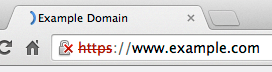
    And all SHA-1 SSL certificates expiring on or after January 1 2017 will be treated as ‘affirmatively insecure’. In this, a red cross and red strike-through is displayed on the URL, as shown in the image below:

    chrome version 41

Here is an easy-to-follow chart that shall help you understand the result of the browser-SSL interaction under Google’s new policies:

Example Dates
Chrome Beta Version Dates SHA-1
up to Dec 31 2015
SHA-1
Jan 1 2015 to Dec 31 2015
SHA-1
Jun 1 2016 to Dec 31 2016
SHA-1
Jan 1 2017
Advisable Signature Algorithm
Chrome Version 39 Sept 2014 SSL certificate pad lock SSL certificate pad lock SSL certificate pad lock chrome version 39 error SSL certificate pad lock
Chrome Version 40 Nov 2014 SSL certificate pad lock SSL certificate pad lock chrome version 39 error chrome version 40 error SSL certificate pad lock
Chrome Version 41 01 2015 SSL certificate pad lock chrome version 39 error chrome version 39 error chrome version 41 error SSL certificate pad lock

How to View an SSL Certificate in Google Chrome

Understand SSL Certificate in Google Chrome Web Browser

Google Chrome is a web browser developed by Google. It was released in 2008, and today, its feature-rich profile and innovative aspects have helped it attain the enviable position of being the most popular web browser in the world. As per one survey in July 2014, about 45% of web users prefer Google Chrome over other options available on the market.

The Google Chrome web-browser is efficiently capable of securing online data. By default, the SSL security in Google Chrome is set to the medium, keeping the level not too strict and neither too open. It is advisable for users to not make any changes to these default settings unless required.

Installation Procedure: How to View SSL certificate in Chrome

The installation procedure given below is based on the assumption that users have already downloaded the root certificate to the network location.

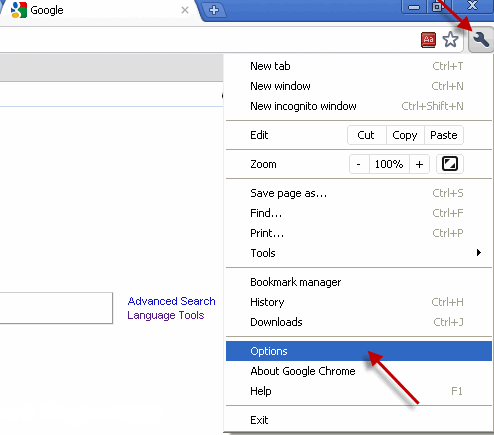
Step 1 – To start with the procedure, first of all, click on the icon of ‘Customize and Control Google Chrome’ menu present on the upper right corner of your screen. See Figure A.

Step 2 – Now, click on ‘Options’ menu.

Google Chrome Browser

Figure A

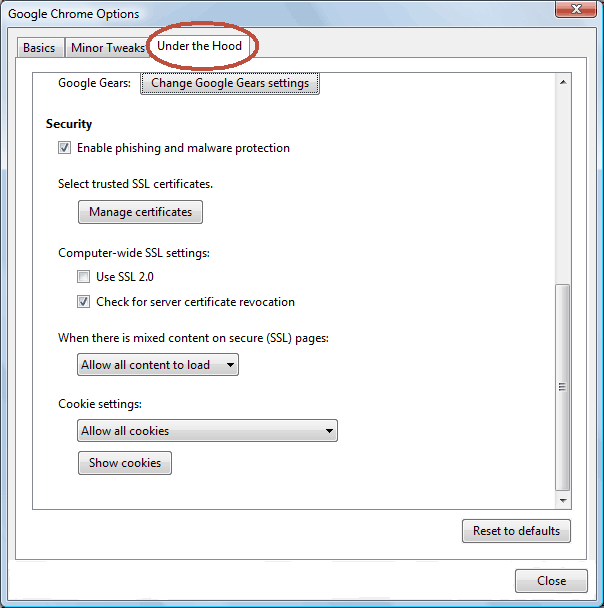
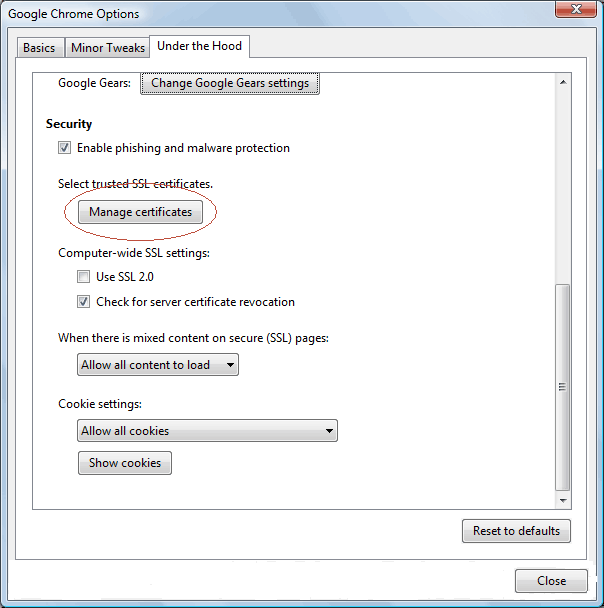
Step 3 – From the window ‘Google Chrome Options’, select the tab ‘Under the Hood’ as shown in Figure B.

Step 4 –In that tab, select the ‘Security’ option. See Figure B.

Certificate Panel

Figure B

Step 5 – Click on the button ‘Manage Certificate’ just under ‘Select trusted SSL certificates’, as shown in Figure C.

Google Chrome Options

Figure C

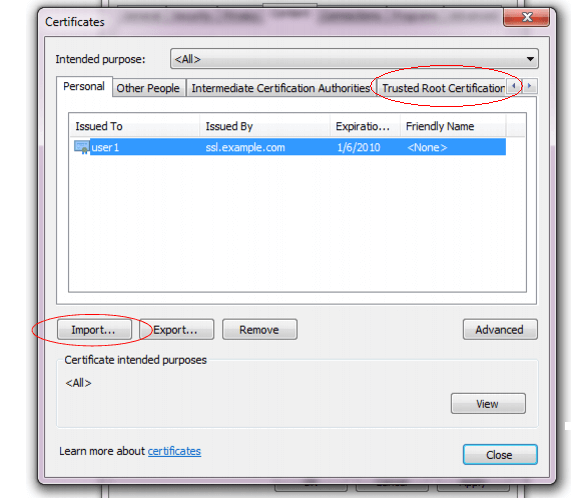
Step 6 – After clicking on ‘Manage Certificates’, the ‘Certificates’ window pops open, where users can import, export or remove the SSL certificates. Now, click on the ‘Trusted Root Certification’ tab and click on the ‘Import’ button as shown in Figure D.

Certificates

Figure D

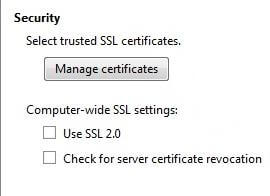
Step 7 – Now, click on the following two check boxes listed below ‘Computer-wide SSL settings as shown in Figure E.

  • ‘Use SSL 2.0 – This is SSL protocol’s older version, which is found to be less secure. In spite of that, there are a few websites that may need visitors to use this version during their browsing session. So, users need to select this option only when you trust the website.
  • ‘Server certification revocation’ – Clicking on this check-box, turns on the real-time verification for the website certificate’s validity, for extra security. A third-party issuer can revoke a certificate if that certificate is noticed to be stolen or compromised.

Security Panel
Figure E

Controlled Display of Mixed Content on Secured Pages

Sometimes, the content displayed on an SSL-secured website comes from unreliable sources. Visitors can easily view such content while the web-page loads and the information is being transmitted. There are many types of malicious software that are known to have the potential to modify such insecure contents and make unauthorized changes on websites.

As per the default setting, whenever visitors’ web-browsers come across a webpage with mixed content, an alert icon iconis displayed at the end of the address bar.
Step 8 – Make the following changes under the section of ‘When there is mixed content on secure (SSL) page”. Users can make changes by choosing any one of the following options in the drop down menu:

  • ‘Block all insecure content’: Choosing this option, all insecure images on a page are replaced by broken image icons, and red boxed replace frames and iframes. Nevertheless, by clicking on ‘Show all content’ link present on the top of the page, users can override this setting for some web-pages during their browsing sessions.
  • Allow insecure images’: This setting loads all the insecure images on a web-page. However, these insecure images are marked for users’ convenience in spotting them.
  • ‘Allow all content to load’: As the name suggests, this setting allows a web-page to load all the web-elements regardless of their security state.

Step 9 – At the end of the procedure, please click on ‘Close’ after making all the changes.

Always on SSL Means Always Confident

Understand How Vital is SSL Certificate for Your Website?

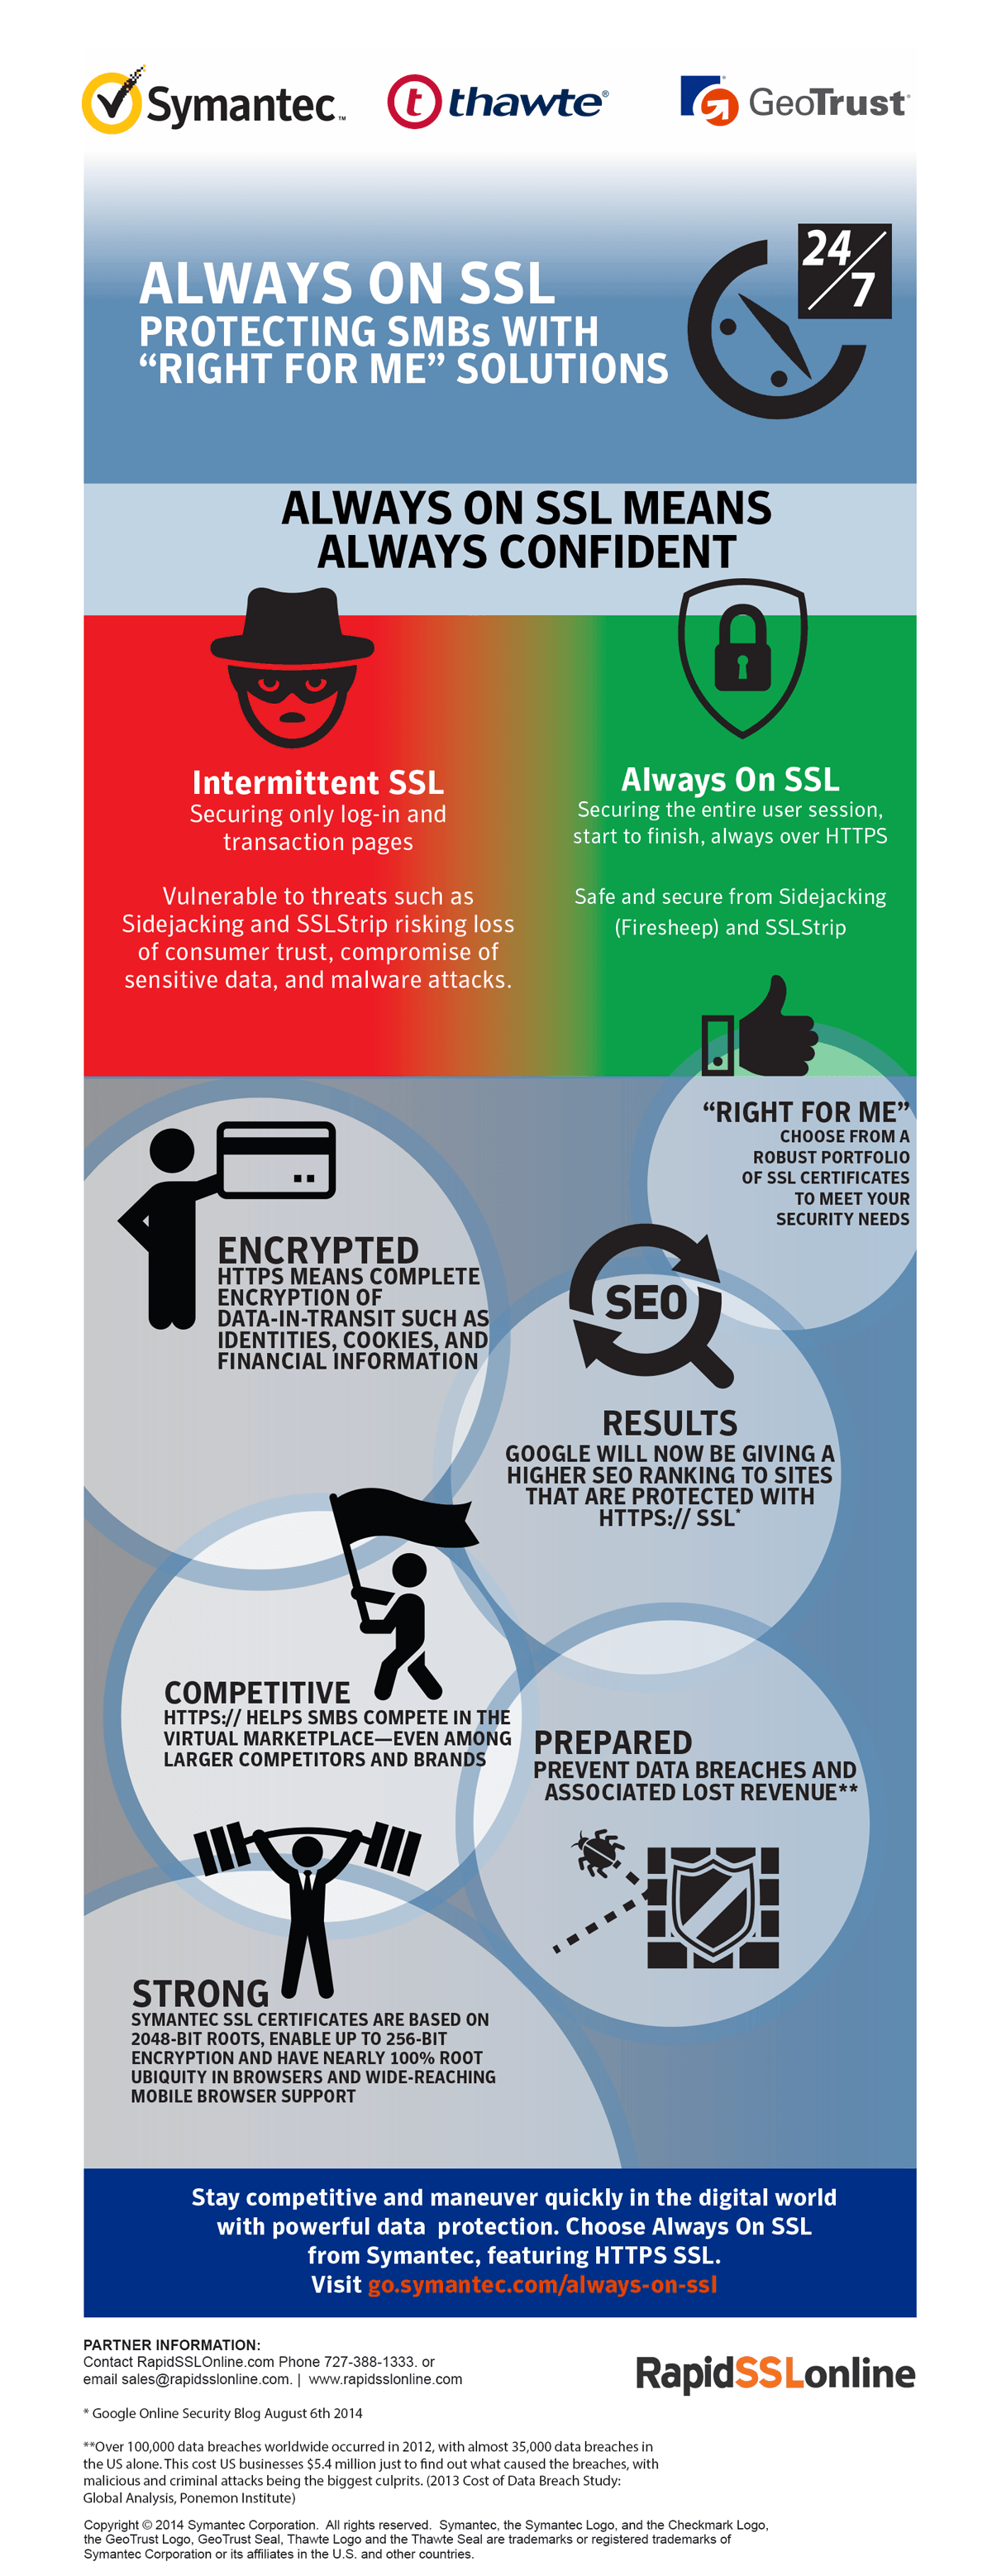
‘Always On SSL’ by Symantec™, is a critical security measure for all the website owners who are looking to secure the entire user experience. You can now authenticate the identity of the website along with total protection against various cyber attacks like sidejacking, malicious codes, cyber hacking etc. Read on to find out more on why it’s advisable to adopt ‘Always On SSL’.

Always on SSL Means Always Confident

SSL Installation Guide for Nginx Web Server

SSL Certificates Installation Guideline for Nginx Web Server

First of all, create a ‘Certificate Bundle’ to get started with the procedure of SSL installation in Nginx. For creating the bundle, each certificate (SSL certificate, Intermediate certificate and Root certificate) needs to be in the PEM format.

  • In a plain text editor, open each certificates.
  • Now proceed by creating a new document in a plain text editor.
  • Your SSL Certificate
  • Intermediate SSL certificate
  • Root SSL Certificate

This completes your file and its format should be as follows:
 

-----BEGIN CERTIFICATE-----
#Your SSL Certificate#
-----END CERTIFICATE-----
-----BEGIN CERTIFICATE-----
#Intermediate Certificate#
-----END CERTIFICATE-----
-----BEGIN CERTIFICATE-----
#Root Certificate#
-----END CERTIFICATE-----

 
This newly-created certificate bundle should be saved in a ‘.crt’ format.
After saving it properly, upload the certificate bundle along with the private key to a directory on the Nginx server.
After that, edit the Nginx virtual hosts file.

For that, open the Nginx virtual host file for the website you intend to secure. In case you want your site to be accessible through both, secure (https) and non-secure (http) connections, you need to have a server module for each connection type.

Now proceed by making a copy of the existing non-secure module and pasting it below the original. Add the lines in the format given below:

server{
listen 443;
ssl on;
ssl_certificate /etc/ssl/your_domain.crt;
ssl_certificate_key /etc/ssl/your_domain.key;
server_name your.domain.com;
access_log /var/log/nginx/nginx.vhost.access.log;
error_log /var/log/nginx/nginx.vhost.error.log;
location / {
root /home/www/public_html/your.domain.com/public/;
index index.html;
}
}

 
Please note it is very important to make sure you adjust the file names so as to match your certificate files.

  • Ssl_certificate should be your primary certificate which is combined with the root and intermediate certificate bundle created in previous steps. For example, your_domain.crt.
  • When you generate the CSR, ssl_certificate_key should be the key file that is created.
  • Now restart Nginx.
sudo /etc/init.d/nginx restart


NGINX Wildcard SSL Certificates

RapidSSL Logo
NGINX Wildcard SSL Certificate allows multiple servers subdomains security with single SSL certificate.


Mobile Cloud Computing – The Future of Mobile Applications

Understand Cloud Computing for Mobile Applications

Mobile Cloud Computing, or MCC, merges the fast-growing Cloud Computing Applications market with the ubiquitous smartphone. One of the most ground-breaking blends of modern-day technologies, MCC has proved itself to be highly beneficial to all mobile users and cloud-based service providers as well.

Read More Mobile Cloud Computing – The Future of Mobile Applications