All posts by Adam Thompson

How can you escape a cyber attack on your smart-phone?

Stay Secure on Your Smart-Phone with Premium Cyber Attack Security Tips

We all know that the ‘PC era’ is quickly being replaced by the ‘Smart-phone’ era, since we see almost every hand attached to a smart-phone these days. PC sales have persistently nose-dived, ever since users were introduced to smart-phones and their advanced capabilities. These mobile devices, being less expensive and more convenient when compared to clunky old desktop computers, almost immediately became a striking alternative to accessing the Internet anywhere, anytime.

Read More How can you escape a cyber attack on your smart-phone?

EBay database hacked, asks users to change passwords

Lately cyber-criminals seem to be obsessed with the trend of hacking into users’ accounts on popular websites by stealing their login credentials and passwords. Last fall it was ‘Target Corp’ being hacked followed by ‘Adobe Systems Inc’ with compromised login credentials. This year, after the web-link shortening service, Bitly being attacked in May, online shopping giant, EBay is the latest name to join the list.

On Wednesday, May 22 2014, EBay advised its 145 million registered users of its website to change their passwords following a security breach in its database having encrypted passwords and some other non-financial data.

The online shopping giant provided some information about how the attackers hacked the site. It said they were successful to gain access in to the corporate network by compromising some of the employee’s login credentials, EBay informed. However, users’ passwords of EBay’s payment network PayPal weren’t compromised in this attack, clarifies EBay’s spokeswoman.

According to EBay, the database compromise was detected about 2 weeks ago though it occurred somewhere between late February and early March. The company chose not to inform its users right away as it investigated the extent of the attack. The spokeswoman said no group has yet claimed the attack’s responsibility and that the company has found no evidence indicating an unauthorized access to financial or credit card information as EBay stores that sensitive data stored separately. The hacked database consisted of passwords, email ids, birth dates, postal addresses and phone numbers. Following the news about the attack, EBay’s shared dwindled at Nasdaq on Wednesday.

EBay says the breach in its network is in no way related to the flaw in encryption tools ‘Heartbleed’, as recently detected by security researchers. Also, the company advises all its users who have set identical passwords for other sites to change all those passwords as well.

Chinese Government bans Windows 8 installation of on government computers

Chinese Government bans Windows 8 installation of on government computers

Chinese government has excluded Windows 8 Operating System from being installed on new computers, much to Microsoft’s ‘surprise’.

China’s decision to exclude Windows 8 from its new government computers came as a major blow to the US’ Microsoft, the technology company, which has long been dealing with the sales woes in this Asian country. On the website of Central Government Procurement Center, in a short statement about a specific class of energy-saving products, the agency noticed that the new government computers were prevented from having Windows 8 installed.

Sources find it interesting as this news comes in at a time when there is already animosity between US and China. On Monday, US pressed charges against several Chinese government officials for allegedly hacking networks in the US, to which China sharply responded by saying that US itself has engaged in cyber- spying against China. However, the point to be noted here is that the Chinese government’s decision to nix Windows 8 was taken last week, before the US accusation.

But, with seemingly mysterious reasons involved behind the ban, even till date the Chinese government has not explained its motives behind banning Windows 8 from the computers in the public sector. However, China’s official news bureau, Xinhua claims the ban is a result of Microsoft officially ended its ties of 13 years with Windows XP. And as noticed by Reuters, news bureau Xinhua has also vaguely cited reasons like ‘security measures’ and ‘effort to save energy’ as a potential foundation behind the ban. But the relation between Windows 8 usage and saving energy is found to be highly unclear. However, there is no further elaboration on this front from Xinhua or the Government of China. Xinhua also notes that Chinese government intends to develop and use its own Linux-based Operating System.

As per the statements given out by Microsoft, although it was ‘stunned’ by the decision of excluding Windows 8 by the Chinese government, the company would continue to provide Windows 7 to several Chinese government customers. As of now, which OS would be replacing the still-widely used Windows XP, is still uncertain.

Bitly accounts got hacked: What to do next?

Stay Safe and Secure for Your Bit.ly Accounts

Bitly Hacked

The URL shortening service, Bitly happens to be the latest victim of the hackers. As per its CEO Mark Josephson’s latest blog update: an ‘Urgent Security Update’, they have found reasons to believe that their users’ data has been compromised. This vulnerable data consists of e-mail addresses, secured passwords, OAuth tokens and API keys.

Josephson mentions in the blog that they don’t have any indication that any of the accounts have been accessed without the permission. But as a preventive measure, the company has requested all the users to reset their account passwords. In addition to that, Bitly has also taken precautionary steps like disconnecting the social media profiles to ensure the security of all the accounts. The users generally signing in through their Twitter or Facebook accounts would be required now to reconnect their accounts.

This security breach in Bitly accounts might be a lucrative opportunity for the cyber-criminals, as most of the Bitly users link their accounts to Facebook and Twitter profiles. This opens the door for sending spam links and campaigns through this service. However, there is no confirmation of any such incidence as yet from Bitly. Also, as a precaution, if you are using the same password for Bitly and any other account, you need to change that password on the account right away. As there is a risk that the compromised Bitly password can be used to gain access to your other accounts.

Now, as per the blog update, the most important step for all the Bitly users would be to reset their API key and OAuth token. Please find below all the step-by-step instructions provided by the company, to help you reset your API key and OAuth token:

1) First of all, log in to your account and click on ‘Your Settings,’ then the ‘Advanced’ tab.

2) Now, at the bottom of the ‘Advanced’ tab’s menu, select ‘Reset’ next to ‘Legacy API key.’

3) Copy down your new API key and change it in all applications. These may include social publishers, share buttons and mobile applications.

4) Now reset you password by going into the ‘Profile’ tab.

5) Disconnect and reconnect any applications that use Bitly. You can now check which accounts are connected under the ‘Connected Accounts’ tab in ‘Your Settings.’

Apart from providing the basic information about the security breach and few precautionary steps to be taken by the users, Bitly chose not to explain how it found out about the breach in the privacy of customer accounts. Moreover, the company has shared no details about exactly which information the hackers might have gained access to.

It is important to note here that this security breach will not be affecting users who use Bitly just as a basic link-shortening service without signing in. However, it does affect all the registered users who use the tools like saved links, stat tracking and social network sharing. The attack can also potentially pose as a threat to all the website publishers who use Bitly to track and share story links.

Josephson signs off the blog post with an apology for any inconvenience caused and claims that their team is working hard to make sure all the accounts are secure and that they take users’ security very seriously. Users can check out latest updates on their Twitter feed: @Bitly. And for any account specific questions, they can send e-mails on [email protected]. 

Little Guide to Help you Choose a SSL Certificate Authority!

The Norton Secured Site seal is no longer offered starting Oct. 16, 2023.

Tips to Choose The Best Certificate Authority (CA)
about certificate authority

Over the years, as the arena of e-commerce flourished, the SSL industry as well, expanded along with it. So much so, that it is now impossible to imagine a safe and successful e-commerce website without an SSL certificate safeguarding it. Whether it’s the new best-seller you are buying from amazon.com or accessing your bank account online, an SSL certificate is always there to safeguard the information you submit online. Just as important as SSLs are the Certificate Authorities (CAs), a trusted third party organization that issues digital certificates. Their duty is to authenticate the identities of the two parties exchanging information. That is the reason all the CAs hold significant importance in data security and e-commerce industry.

This extensive usage of SSL certificates have given way to CAs to come up with SSL certificates with myriad features and characteristics. In fact, the website owners now have too many options to choose from when it comes to zeroing down on an SSL certificate as per the website requirement and a Certificate Authority (CA) issuing one. There are many factors like costing, features etc which need to be considered before choosing an SSL certificate and a CA. Here, we help you get acquainted with few of the major names in the CA industry: Symantec, GeoTrust, Thawte and RapidSSL.

Symantec
Symantec SSL Logo

Symantec was established in the year 1992, since then it has evolved to become one of the leading SSL certificates’ suppliers across the world. Operating in more than 50 countries across the world, Symantec today houses around 18,500 employees. They are good at providing online security, storage and systems management solutions to support their customers who range from online consumers and small scale businesses to large global organizations. Symantec helps them secure and manage their online businesses.


Why Symantec

Many organizations and e-commerce merchants have chosen Symantec to be their first choice for SSL certificates. Here, we put together few reasons for you to have a look at:

  • Outstanding Online Customer Support: Prompt 24/7 customer service is complemented by Express Renewal and 30-day money back guarantee
  • Norton Secured Seal: This seal is the most trusted mark on the Internet and is viewed more than half a billion times per day across 170 countries. Symantec’s Seal-In-Search displays Norton Secured Seal next to the links
  • More than a Digital Certificate: It helps drive traffic to the website and reduce abandoned transactions. Its features like Norton Security Seal, Search-In-Seal technology work in sync to assure customers that the site is safe and secured.
  • Malware Scanning: Symantec SSL certificate protects your website from malware by performing daily website malware scanning

Products

Product Name Issuance Time Validation Site Seal
Secure Site Pro with EV 5 Days Organization Dynamic
Secure Site with EV 5 Days Organization Dynamic
Secure Site Pro 2 Days Organization Dynamic
Secure Site 4-5 Days Organization Dynamic
Code Signing Certificate 2-3 Days Organization N/A
Symantec Safe Site 2-3 Days Organization Dynamic
Symantec Secure Site Wildcard 1-2 Days Organization Dynamic


Site Seal Importance

Symantec’s Norton Secured Seal is the most trusted mark on the Internet. It is viewed half a billion times per day across about 170 countries. It enables you to grow more traffic and maximize web sales by letting the visitors know that they are browsing and buying from a secured site. More than 40 million desktops using Norton Safe Web across the world see Norton Secured Seal next the trusted websites in the search results.

GeoTrust
GeoTrust SSL Logo

Established in 2001, GeoTrust is headquartered in California, US. GeoTrust is world’s second largest digital certificate provider. Previously owned by VeriSign, today GeoTrust is owned by Symantec. More than 100,000 customers across 150 countries rely on GeoTrust to secure their online transactions and websites. Digital certificates and trust products by GeoTrust enable businesses and organizations maximize the security of any web-based transactions at cost-effective rates.


Why GeoTrust

  • Quick Turnaround Time: GeoTrust helps you get an SSL certificate in real time. One can even use, manage and renew an SSL very conveniently.
  • Cost-efficient: GeoTrust have a wide range of excellent quality certificates that are sold at market-low prices. Also the SAN-enabled certificates offer inexpensive and flexible multi-domain options.
  • Unlimited Server Licensing: A single certificate can secure an unlimited number of servers. Re-issuing is free of cost as well.
  • Diverse Options: GeoTrust houses a variety of SSL certificates that range from simple domain-validated certificates to business-boosting Extended Validated certificates with green address bar.

Products

Product Name Issuance Time Validation Site Seal
GeoTrust QuickSSL Premium SSL 10 Minutes Domain Dynamic
GeoTrust True Business ID with EV 1 to 10 Days Organization Dynamic
GeoTrust True Business ID 2 to 4 Days Organization Dynamic
GeoTrust True BusinessID Multi Domain (SAN/UCC) 1 to 2 Days Organization Dynamic
GeoTrust BusinessID Wildcard SSL 1 to 2 Days Organization Dynamic
Symantec Safe Site 2-3 Days Organization Dynamic
GeoTrust True BusinessID with EV Multi Domain 1 to 10 Days Organization Dynamic
Geo-Trust Web Site Anti-Malware Scan N/A Domain N/A


Site Seal Importance

Customers’ anxieties and concerns tend to heighten as they submit their personal or financial information on websites. But in case of GeoTrust, all these concerns are put to rest by an assuring symbol of GeoTrust Site seal pasted on the web page. It acts like an instant proof for your customers that they are visiting a website that has a stamp of approval by leading Certificate Authorities for safe e-transactions.

It’s advisable to add these Site Seals to your home page, payment page and other such pages of website where visitors need to verify the website’s authenticity.

Thawte
Thawte SSL Logo

Established in the year 1995 by Mark Shuttleworth in South Africa, Thawte has quickly grown into one of the most trusted Certificate Authorities. In fact, it was the first Certificate Authority to issue SSL certificates to public entities outside the US. Till date, Thawte has issued more than 945, 000 SSL certificates and code signing certificate across 240 countries.

Thawte was acquired by VeriSign in the year 2000 and continues to prosper as a separate brand. Popular among the small businesses throughout Europe and Asia, Thawte is also chosen by millions across the world for securing their web pages.


Why Thawte

  • It accounts for about 40% of global market
  • First to provide multi-lingual trust seals, which builds confidence in customers by verifying
  • Enables more people to navigate the web safely on their own
  • Advanced SSL protection that includes rigorous authentication process and strong infrastructure

Products

Product Name Issuance Time Validation Site Seal
Thawte SSL Web Server with EV 1 to 10 Days Organization Dynamic
Thawte SSL 123 10 Minutes Domain Dynamic
Thawte SSL Web Server 1 to 2 Days Organization Dynamic
Thawte SGC SuperCerts 1 to 10 Days Organization Dynamic
Thawte Wildcard SSL Certificate 1 to 2 Days Organization N/A
Thawte Code Signing Certificate 2-3 Days Organization N/A
Thawte Code Signing Individual 2-3 Days Organization N/A


Site Seal Importance

Thawte was the first one to come up with the concept of a Multi-Lingual Site Seal which is now available in about 18 different local languages. They provide visual reassurance that Thawte has verified the site’s identity and that it’s safe to carry out transactions on that site as they are secured by SSL. The seal is displayed within 2 hours of installing.

On clicking the Trusted Seal on web pages, a seal verification page opens in a new browser window and shows the verified domain name; certificate authority that performed the authentication; and the validity period. In case of full organization validation and Extended Validation, the SSL certificate also displays the organization’s name and location.

Thawte recommends adding the seal script to secured home page, buy page, sign-in page, and all other pages in your secured domain where customers need assurance.

RapidSSL
RapidSSL Logo

SSL certificates by RapidSSL are an apt choice to secure small and medium sized businesses and web pages having limited traffic. RapidSSL is owned and operated by GeoTrust, Inc and is focused on providing websites of small/medium enterprises or businesses (SME) with strong protection of 128/256 bit.

RapidSSL certificates are Domain Validated (DV) and issued within few minutes. Their economical range of SSL certificates is very advantageous to SME e-commerce businesses. Their root certificates are compatible with 99% of browsers. A static trust mark of RapidSSL’s site seal is provided that can be displayed on the website along with other display cues like https URL and a closed padlock icon.


Why RapidSSL

RapidSSL’s inexpensive range of SSL certificates happens to be the principle reason behind it being chosen over other brands, especially by small and medium e-commerce websites. There are several other reasons as well which can be listed down as follows:

  • Instant issuance
  • Complete automated validation
  • Root certificate has 99$ browser recognition
  • Strong 256-bit encryption
  • $10,000 warranty

Products

Product Name Issuance Time Validation Site Seal
RapidSSL Certificates Immediate Domain Static
Rapid SSL Wildcard Immediate Domain Static
Free Rapid SSL 10-15 minutes Domain Static


Site Seal Importance

RapidSSL offers all its clients to display a Site Seal on its (client’s) website. A website seal is of great importance as it ensures website trust and establishes credibility to all the potential customers visiting the website. RapidSSL decided to release an updated version of its logo in the year 2011. It’s a GIF with rotating display of ‘Secured by RapidSSL’, its encryption strength and warranty. This is an entry level certificate that would provide basic validation and authentication of your website. This certificate is perfect for you if you are looking to set up basic web presence and need an SSL certificate right away.


Conclusion

And so, choosing a Certificate Authority can get a bit confusing as there are too many factors involved that are to be taken into consideration. But ultimately the CA you end up choosing has to have the framework, product range and costing that perfectly fit websites’ security needs and your budget at the same time.

Guide on Installing SSL on Cisco Secure Access Control Server (ACS)

SSL Certificate Installation Guideline for Cisco Secure ACS

Cisco Secure Access Control Server is an access policy control platform which helps meet the regulatory and corporate requirements. It helps improve productivity and at the same time supports multiple scenarios like:

  • It authenticates administrators, authorizes commands and provides an audit trail.
  • Works efficiently with VPN and other remote network access devices to enforce access policies.
  • It authenticates and authorizes wireless users and hosts.

Cisco Secure Access Control Server (ACS) uses HTTP by default for all its administrative sessions. Install an SSL certificate follow the steps given below:

Step I – Intermediate Certificate Installation

  • Click on System Configuration after logging on to ACS
  • Click on ACS Certificate Set-up
  • Now select ACS Certification Authority Setup
  • Enter the path and file name of the Intermediate certificate in CA certificate box
  • Now click on Submit

Step II – Primary Certificate Installation

  • Save the Primary certificate, received from your Certificate Authority (CA) as mydomain.com.cer
  • Click on System Configuration and login to ACS
  • Now click on ACS Certificate Setup
  • Select Install ACS Certificate
  • Now proceed by choosing Read certificate from file. Enter the path and file name of SSL server certificate which you saved as mydomain.com.cer. Fill out the remaining form and click Submit
  • Select System Configuration > Service Control and click on Restart button

Step III – Verification

  • Please Click Here to verify your newly installed SSL certificate for any error or inaccuracies, if any, occurred during the installation procedure.

If you are using the different version of CISCO ACS, then we have made it more simple for installing an SSL certificate. Check other guides of SSL installation.

How to Reduce Vulnerabilities & Online Malware Attacks on Android Devices

Understand Online Vulnerabilities to Stay Secure for Android Devices

These days, “Mobile Vulnerabilities” and ‘Malware Attacks’ seem to be dominating the mobile threat landscape. Such threats have plagued the security scenario, more so in the case of Android devices. Often we hear about updates from the security industry pointing out new vulnerabilities found in Android OS, more sophisticated and hazardous than the previous version. Apparently, cyber-criminals are successfully finding intuitive ways to exploit this OS on these devices.

Read More How to Reduce Vulnerabilities & Online Malware Attacks on Android Devices

Step-by-Step Guide on how to install SSL certificates on a BEA WebLogic Web Server

SSL Certificates Installation Guideline for BEA Web Logic Web Server

BEA WebLogic Web ServerBEA System’s WebLogic is one of the best e-commerce online transaction processing (OLTP) platforms. It’s a server software application which is efficiently developed to connect users in a distributed computing environment to assist the integration of mainframe applications, distributed corporate data and applications.

WebLogic server’s main features are the connectors which helps enable an inter-operation of legacy application on any client along with server applications, Enterprise JavaBean (EJB) components, resource pooling and connection sharing. This makes the applications capable enough to expand and cope with the increased use. An administration console with a user interface eases management tasks like common security features; such as, Secure Socket Layers (SSL) which make applications and transactions very secure by encrypting data transmissions with mechanisms for proper authentication and authorization.

Installing an SSL certificate properly is the best way to maintain authorization secure environment for data transmission. Here’s a step-by-step guide on how to successfully install an SSL on WebLogic.

Installation procedure for SSL Digital Certificate in WebLogic

1. First of all, download from your account the your_domain_com.p7b certificate file. It can be downloaded from the tab of “My Orders” by clicking on the order number and then the blue download link.

2. To install the certificate file to your keystore, run the following command:

keytool -import -trustcacerts -alias server -file your_domain_com.p7b -keystore your_domain.jks

A confirmation message pops up after this which reads “Certificate reply was installed in keystore” after which it asks if you want to trust the certificate, choose ‘y’ or ‘yes’.

The procedure of installing this file loads all the necessary certificates to your keystore. To use it, all you need to do is configure your server.

How to Configuring the Keystore in WebLogic

1. Expand the “Servers” node on your WebLogic server and choose the server you wish to configure.

2. After that, go to Configuration >> Key-stores and SSL
Several default key-stores or previously installed key-stores shall be displayed under ‘Keystore Configuration’.

3. Click the ‘Change…..’ link located under ‘Keystore Configuration’ to enable your new keystore.

4. Select ‘Custom Identity and Java Standard Trust’ as your keystore configuration type. Click on Continue.

5. Enter the full path to the your_domain.jks file on your server under ‘Custom Identity Keystore File Name’.

6. Choose jks for ‘Custom Identity Keystore Type’

7. The ‘Custom Identity Keystore Passphrase’ should be the password that you specified while creating the keystore.
In case you forgot the password, you will have to start the procedure of creating your keystore right from the start.

8. You will, once again be asked to enter the keystore password and confirm it.

9. Click ‘Continue’ and then Finish.

10. Now you got to go back to ‘Servers’ node and select the server you are configuring.

11. After that, go to Configuration >> Key-stores and SSL>> Click ‘Change…..’ link that lay under ‘Keystore Configuration’

12. On the page of ‘Configure SSL’ choose ‘Key Stores’ as the procedure in which identity and trust is stored for the WebLogic server.

13. Specify the ‘Private Key Alias’ and the ‘Passphrase’ which were used while creating your keystore.
‘Server’ is your alias if you are following the set of instructions mentioned here and the Keystore password is your passphrase.

14. Click Continue, then Finish
You will now have to reboot the WebLogic server.

15. Your keystore should now be installed and enabled.

Your browsers’ padlock icon should be displaying the locked position if you have successfully installed the SSL certificate.

SSL Certificate Installation in Apple Mac OS X Server

Apple Mac OS X Server SSL Installation

The followings steps make for a quick guide to help you install an SSL certificate in Apple Mac OS X Server.

Step 1

Once your order is issued, store the yourhostname.zip file into your server, and extract both your Primary Certificate (yourhostname.cert) and Intermediate Certificate (certificateauthority.crt) in the same folder.

Step 2

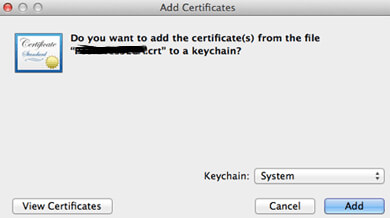
Now, Double click on Intermediate Certificate and choose import option from the pop-box of ‘Add Certificate’, then select ‘System’ option from ‘Keychain’ drop down menu and click on ‘Add Button’ to perform the import process.

Add Certificate KeyChain Confirmation Mac OS Apple Web Server

Note: For the next step of Import process, you need to add administrator credential to validate changes.

Step 3

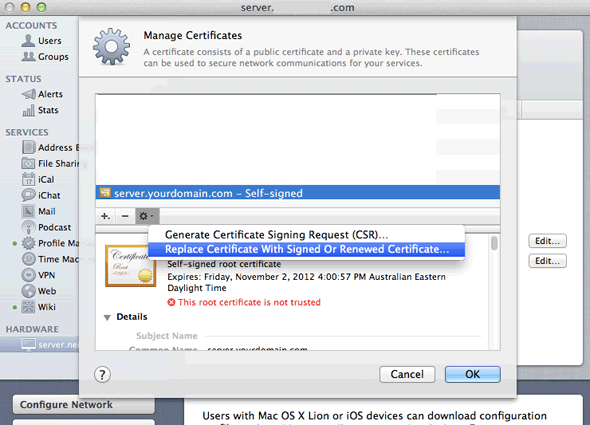
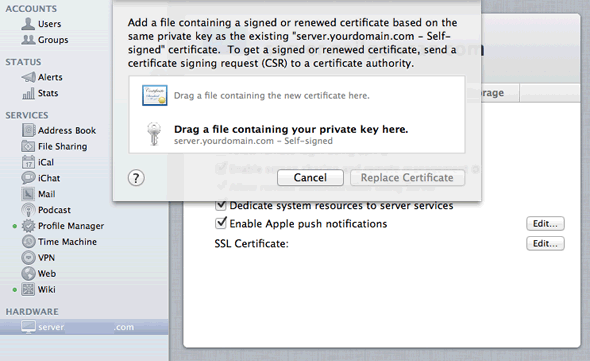
After import process, open your Apple Mac OS X Server and then click on ‘Certificates’. Now select the setting option and choose ‘Add Signed or Renewed Certificate from Certificate Authority’ in that drop down menu.

server replace cacert

Step 4

Once you choose the option ’Add Signed or Renewed Certificate from Certificate Authority’ from the Settings, it will show all the details about the existing certificate or the new certificate. Now you have to drag your Primary Certificate (yourhostname.cert) into the pop window, which you have seen while selecting the option ’Add Signed or Renewed Certificate from Certificate Authority’ from setting.

Step 5

Now click the ‘OK’ button when you complete Primary Certificate (yourhostname.cert) drag and drop process.

Server Replace CAcert 2

That’s it. Your SSL Certificate is now installed on the Apple Mac OS X Server.

Additional Subject in Apple Mac OS X Server SSL Installation Process

1. Allocation of SSL Certificate to Mail Services

Click on the ’Mail’ option which you can see on the left side of window. Now, open setting options of mail, and then click on Advanced and then Security option. From Security option, you can assign installed SSL Certificate to SMTP or IMAP Services.

2. Allocation of SSL Certificate to Web Services. Please refer following steps:

  • Open web server and select your website
  • Choose a website from your list for which you want to add certificate
  • Click on the security tab option and the checkbox to Enable Secure Sockets Layer (SSL)
  • Now choose the certificate and then restart your web server

SSL certificate is now installed to your Mail & Web Services.

SSL Installation Resources

1. Check your SSL certificate installation with just one click using SSL checker tool.

https://www.rapidsslonline.com/ssl-tools/ssl-checker.php

2. Read documentation of Apple Mac OS X SSL Installation

2. Video Guide: Generating a CSR for Apple’s Mac OS Server 5.0